Step 1
Assess
Understand your current state, risks and priorities.
Built for banks, regulators, governments and growing organizations. Connecting CIO and CISO leadership with technology strategy, cybersecurity expertise and digital transformation.
You need proven technology and security leadership at the table, without the full-time cost. As your virtual CIO or CISO, we set strategy, report to your board and direct your teams and vendors on a flexible basis.
Independent, board-level counsel on technology investment, cyber risk appetite and organizational resilience.
Enterprise technology, cloud and AI strategies aligned to business goals and translated into costed, multi-year roadmaps.
Make informed technology purchases through clear requirements, well-structured tenders and independent vendor evaluation and selection.
Independent maturity, risk and compliance assessments benchmarked against ISO 27001, NIST CSF 2.0 and regulatory requirements.
Design and implementation of enterprise security programs based on ISO 27001 and NIST CSF 2.0, through to certification readiness.
Managed testing through vetted partners, or independent oversight of your provider, with findings prioritized into a remediation plan.
Align technology investment with your priorities through digital strategy and transformation roadmaps, including low-code and no-code approaches where they improve service delivery and automation.
Operating model design and review, ITIL-aligned service management, portfolio governance and vendor performance management.
Cloud strategy and FinOps, enterprise architecture, data governance and responsible AI frameworks.
Who we serve
We advise public and private organizations in Kenya, throughout East Africa and internationally, with an established record of leadership in regulated sectors.
Cyber risk oversight and regulatory readiness to protect customers and strengthen financial service resilience.
Security governance and ISO 27001 readiness to safeguard sensitive information and critical institutional operations.
Digital strategy, data protection and vendor oversight for dependable, accountable public services.
Secure modernization to protect sensitive health information and support continuity in care and health reporting.
Technology strategy and cyber readiness that support growth, program delivery and audit preparedness.
How we work
Step 1
Understand your current state, risks and priorities.
Step 2
Agree a clear, prioritized roadmap.
Step 3
Guide delivery, governance and vendors.
Step 4
Build lasting capability in your team.
Assess your current maturity, identify gaps and define a clear path to your target state.
Develop a multi-year IT and cybersecurity strategy, with a roadmap to deliver its outcomes.
Dedicated CIO or CISO leadership for a set number of days each month.
Focused sessions for leadership and technical teams.
Meet our founder
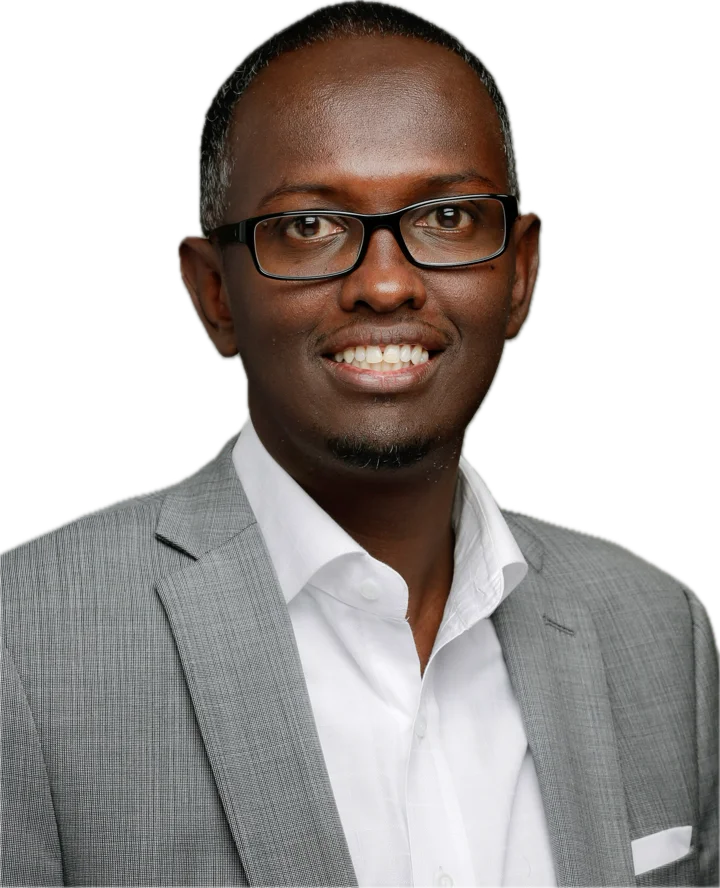
30+ years in technology and cybersecurity
Frameworks: ISO 27001 · NIST CSF 2.0
Founder & Principal Advisor
He leads Strativa’s advisory work, drawing on a trusted network of specialist partners where an engagement requires it.
His career spans more than 30 years in technology and cybersecurity, starting as a network and security engineer and rising through increasingly senior roles, including Head of Enterprise Technology and Chief Information Security Officer, in public and private sector organizations.
He has advised organizations and boards on technology and cyber risk, led organizations to ISO 27001 certification, delivered large-scale cloud migrations and launched enterprise AI strategies. Strativa brings that experience to institutions across East Africa and internationally.
Explore Hassan’s career
Our vision
Our mission
Independent judgement. Vendor neutrality. Your interests come first.
International standards, applied locally.
We build your capability, not dependency.
Measurable outcomes, not reports on shelves.
Your data and confidentiality come first.
Insights
Analysis of the technology decisions, security challenges and governance priorities facing organizations today.
Security tools are controls, not a strategy. An ISMS gives your organization the governance and accountability to manage cyber risk.
Read analysisWhy SMS verification alone leaves customers exposed, and what banks, SACCOs and digital service providers can do about it.
Read analysisHow a coherent digital strategy turns technology spending into advantage, and what happens without one.
Read analysisContact
A complimentary, confidential 30-minute conversation. We’ll listen to your priorities and explore the right next steps together.
Headquartered in Nairobi, Kenya
Advising across East Africa and internationally